Google is developing a new digital asset custody system to help banks and financial institutions secure cryptocurrency holdings using multi-party computation (MPC). The initiative comes as concerns grow over private-key theft, AI-driven cyberattacks and potential threats from future quantum computers.
Called Google Multi-Party Compute, the service is currently in private preview with selected institutional partners. Google Cloud plans to make it commercially available in early 2027, positioning the company to play a larger role in the security infrastructure supporting institutional crypto adoption.
The technology was highlighted ahead of the Digital Asset Security and Multi-Party Computation Symposium in New York on October 28. Alphabet, Google’s parent company, is already using MPC to protect its digital assets on Ethereum and Solana, according to the provided reports.
How Google’s MPC Technology Protects Crypto Assets
In cryptocurrency, control of a private key generally means control of the assets it secures. If attackers obtain that key, they can transfer funds without authorization, and confirmed blockchain transactions are typically irreversible.
For banks and asset managers holding substantial cryptocurrency reserves, a compromised key can therefore cause significant financial losses.
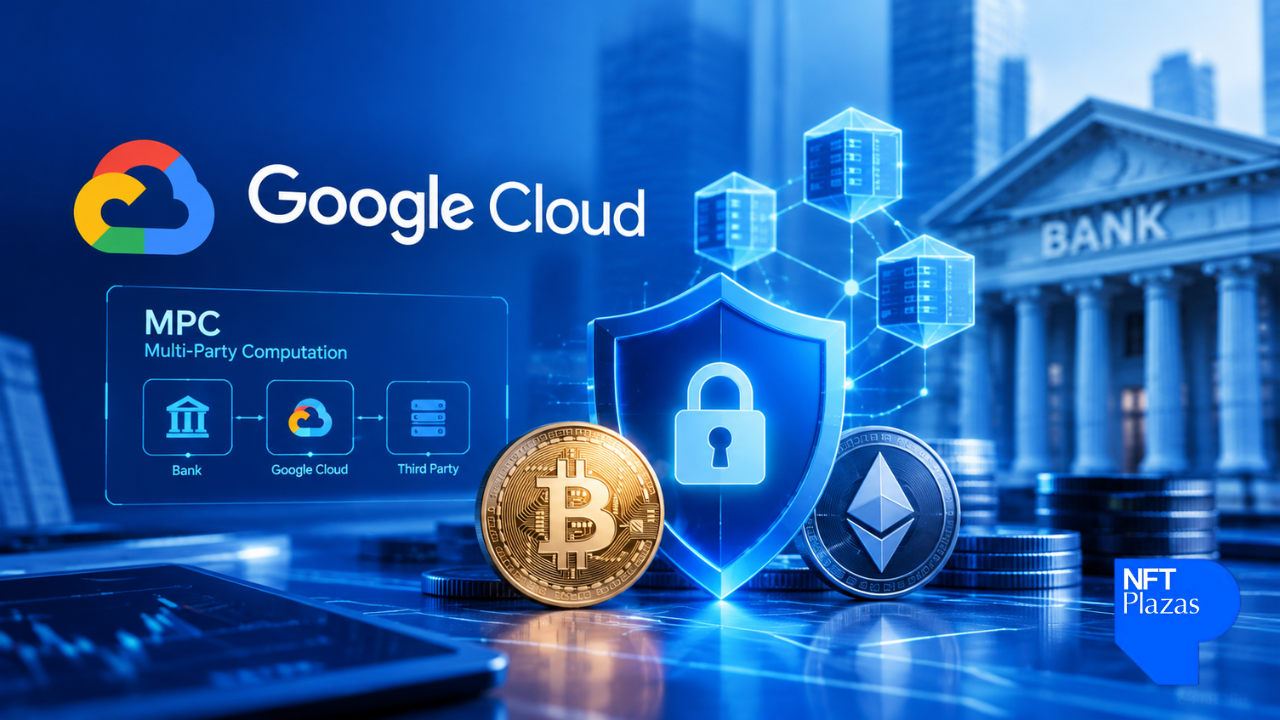
Google’s MPC system addresses this risk by distributing cryptographic key shares across separate environments instead of storing a complete private key in one location.
For example, a financial institution could keep one share on its own infrastructure, another within Google Cloud and a third with a separate provider. When a transaction requires approval, the components work together to generate a valid digital signature without reconstructing the complete private key in one place.
This approach reduces the risk of a single compromised server or account exposing an institution’s entire crypto portfolio.
Google says customers retain control of their keys, and the company cannot access the shares in unencrypted form simply because they reside on its cloud infrastructure.
The system can also support transaction controls, including spending limits, approved destination addresses and internal authorization procedures. These features allow institutions to establish clearer rules governing who can approve transfers and under what conditions.
However, MPC does not eliminate every security risk. Its effectiveness depends on how institutions distribute key shares, configure permissions and manage approvals. If attackers compromise enough authorized participants, they may still be able to execute transactions.
Google Unveils New Crypto Custody Framework to Protect Digital Assets for Banks
AI Raises the Stakes for Crypto Security
Google’s initiative arrives as AI changes the cybersecurity landscape. Attackers can use advanced tools to identify software vulnerabilities, automate parts of their operations and create more convincing scams. Security researchers, meanwhile, are using AI to uncover weaknesses before malicious actors exploit them.
Recent discoveries illustrate the challenge. Researchers have identified vulnerabilities in blockchain systems, including a potential issue involving the XRP Ledger that could have allowed unauthorized token creation if left unresolved.
Ethereum co-founder Vitalik Buterin has also warned that AI-accelerated mathematical research could weaken certain cryptographic systems sooner than expected. He has urged the industry to consider not only quantum computing but also the possibility that AI could accelerate attacks against cryptographic techniques currently considered secure.
For financial institutions, these developments make secure custody increasingly important. Protecting digital assets requires more than storing keys safely. Banks must also manage permissions, monitor transactions and respond quickly when credentials are compromised.
Google’s MPC framework addresses part of this challenge by distributing signing authority across multiple environments, making it harder for a single compromised component to authorize an unauthorized transfer.
Quantum Computing Presents a Longer-Term Threat
Quantum computing presents another potential challenge for blockchain security. Powerful enough quantum computers could eventually undermine some cryptographic methods used to protect digital assets.
Although no quantum computer has demonstrated the ability to break Bitcoin’s cryptography at scale, researchers are examining which holdings could be vulnerable if the technology advances.
Estimates cited in previous research suggest that approximately 6.9 million Bitcoin could face potential quantum-related risks because their public keys have been exposed.
This does not mean those Bitcoin can be stolen today. The risk depends on the development of sufficiently powerful quantum computers and the protections in place when that capability emerges.
MPC can reduce certain risks associated with compromised credentials, but it does not automatically make a wallet resistant to quantum attacks. The cryptographic algorithms themselves must also withstand potential threats.
Google’s longer-term security strategy will therefore need to account for cryptographic upgrades, including post-quantum techniques designed to resist attacks from quantum computers.
Competition Heats Up in Institutional Crypto Custody
Google is entering a competitive market that includes established digital asset security providers such as Fireblocks, BitGo and Fordefi. These companies offer custody infrastructure and transaction security tools designed for institutional clients.
Competition is intensifying as banks, fund managers and other financial firms expand their involvement in cryptocurrencies and tokenized assets. These organizations need infrastructure that can protect digital holdings while meeting internal governance and regulatory requirements.
Institutional crypto custody is becoming more than a secure place to store assets. It is an operational layer supporting trading, settlement and the broader integration of blockchain technology into financial services.
Google’s cloud infrastructure could appeal to institutions seeking to integrate custody controls with their existing technology systems. However, the product remains in private preview, with commercial availability planned for early 2027. Its pricing, full capabilities and institutional adoption remain to be established.
Ultimately, Google’s MPC initiative reflects a broader shift in digital asset security. As financial institutions enter the crypto market, distributing control, strengthening transaction oversight and preparing for emerging threats are becoming essential.
Whether Google can establish itself as a major custody provider will depend on the framework’s reliability, security and ability to meet institutional requirements. Its development nevertheless signals that major technology companies increasingly view digital asset protection as a critical part of the financial system’s evolution.